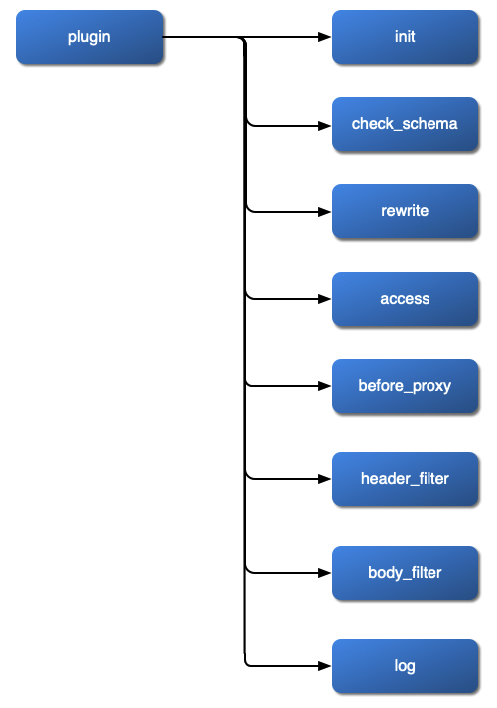
diff --git a/docs/zh/latest/admin-api.md b/docs/zh/latest/admin-api.md
index aae200b88f85..510f50c136b4 100644
--- a/docs/zh/latest/admin-api.md
+++ b/docs/zh/latest/admin-api.md
@@ -370,7 +370,7 @@ Route 也称之为路由,可以通过定义一些规则来匹配客户端的
| filter_func | 否 | 匹配规则 | 用户自定义的过滤函数。可以使用它来实现特殊场景的匹配要求实现。该函数默认接受一个名为 `vars` 的输入参数,可以用它来获取 NGINX 变量。 | function(vars) return vars["arg_name"] == "json" end |
| labels | 否 | 匹配规则 | 标识附加属性的键值对。 | {"version":"v2","build":"16","env":"production"} |
| timeout | 否 | 辅助 | 为 Route 设置 Upstream 连接、发送消息和接收消息的超时时间(单位为秒)。该配置将会覆盖在 Upstream 中配置的 [timeout](#upstream) 选项。 | {"connect": 3, "send": 3, "read": 3} |
-| enable_websocket | 否 | 辅助 | 当设置为 `true` 时,启用 `websocket`(boolean), 默认值为 `false`。 | |
+| enable_websocket | 否 | 辅助 | 当设置为 `true` 时,启用 `websocket`(boolean), 默认值为 `false`。这只是纯粹的协议升级,插件无法访问单独的帧;如果插件需要读取或改写帧内容,请参考 Upstream [`scheme`](#upstream) 下的说明。 | |
| status | 否 | 辅助 | 当设置为 `1` 时,启用该路由,默认值为 `1`。 | `1` 表示启用,`0` 表示禁用。 |
:::note 注意
@@ -679,7 +679,7 @@ Service 是某类 API 的抽象(也可以理解为一组 Route 的抽象)。
| name | 否 | 辅助 | 服务名称。 | |
| desc | 否 | 辅助 | 服务描述。 | |
| labels | 否 | 匹配规则 | 标识附加属性的键值对。 | {"version":"v2","build":"16","env":"production"} |
-| enable_websocket | 否 | 辅助 | `websocket`(boolean) 配置,默认值为 `false`。 | |
+| enable_websocket | 否 | 辅助 | `websocket`(boolean) 配置,默认值为 `false`。这只是纯粹的协议升级,插件无法访问单独的帧;如果插件需要读取或改写帧内容,请参考 Upstream [`scheme`](#upstream) 下的说明。 | |
| hosts | 否 | 匹配规则 | 非空列表形态的 `host`,表示允许有多个不同 `host`,匹配其中任意一个即可。| ["foo.com", "\*.bar.com"] |
Service 对象 JSON 配置示例:
@@ -1022,7 +1022,7 @@ APISIX 的 Upstream 除了基本的负载均衡算法选择外,还支持对上
| desc | 否 | 辅助 | 上游服务描述、使用场景等。 | |
| pass_host | 否 | 枚举 | 请求发给上游时的 `host` 设置选型。 [`pass`,`node`,`rewrite`] 之一,默认是 `pass`。`pass`: 将客户端的 host 透传给上游; `node`: 使用 `upstream` node 中配置的 `host`; `rewrite`: 使用配置项 `upstream_host` 的值。 | |
| upstream_host | 否 | 辅助 | 指定上游请求的 host,只在 `pass_host` 配置为 `rewrite` 时有效。 | |
-| scheme | 否 | 辅助 | 跟上游通信时使用的 scheme。对于 7 层代理,可选值为 [`http`, `https`, `grpc`, `grpcs`]。对于 4 层代理,可选值为 [`tcp`, `udp`, `tls`]。默认值为 `http`,详细信息请参考下文。 |
+| scheme | 否 | 辅助 | 跟上游通信时使用的 scheme。对于 7 层代理,可选值为 [`http`, `https`, `grpc`, `grpcs`, `ws`, `wss`]。对于 4 层代理,可选值为 [`tcp`, `udp`, `tls`]。默认值为 `http`,详细信息请参考下文。 |
| labels | 否 | 匹配规则 | 标识附加属性的键值对。 | {"version":"v2","build":"16","env":"production"} |
| tls.client_cert | 否,不能和 `tls.client_cert_id` 一起使用 | https 证书 | 设置跟上游通信时的客户端证书,详细信息请参考下文。 | |
| tls.client_key | 否,不能和 `tls.client_cert_id` 一起使用 | https 证书私钥 | 设置跟上游通信时的客户端私钥,详细信息请参考下文。 | |
@@ -1048,6 +1048,11 @@ APISIX 的 Upstream 除了基本的负载均衡算法选择外,还支持对上
- 设为 `cookie` 时,`key` 为必传参数,其值为自定义的 cookie name,即 "cookie\_`key`"。请注意 cookie name 是**区分大小写字母**的。例如:`cookie_x_foo` 与 `cookie_X_Foo` 表示不同的 `cookie`。
- 设为 `consumer` 时,`key` 不需要设置。此时哈希算法采用的 `key` 为认证通过的 `consumer_name`。
+APISIX 支持两种不同的方式来代理 WebSocket 连接,二者不能混用:
+
+- Route 或 Service 级别的 [`enable_websocket`](#route),配合 `http`/`https` 的 Upstream `scheme`。这是纯粹的协议升级:`101 Switching Protocols` 握手完成后,由 nginx 自身的 `proxy_pass` 转发原始 TCP 流,没有任何插件 phase 能看到单独的 WebSocket 帧。
+- Upstream `scheme: ws` 或 `scheme: wss`。APISIX 会自己双向解析并代理 WebSocket 帧,插件可以通过 `ws_handshake`、`ws_client_frame`、`ws_upstream_frame`、`ws_close` 这几个 phase 在帧的转发过程中读取或改写它们,具体用法参考[插件开发指南的 "extra phase" 一节](./plugin-develop.md#extra-phase)。如果 Route 或 Service 所属的 Upstream 使用了这个 scheme,`enable_websocket` 会被忽略,因为连接根本不会走到它所配置的那条 `proxy_pass` 路径。
+
以下特性需要 APISIX 运行于 [APISIX-Runtime](./FAQ.md#如何构建-APISIX-Runtime-环境?):
- `scheme` 可以设置成 `tls`,表示 `TLS over TCP`。
diff --git a/t/APISIX.pm b/t/APISIX.pm
index 76dc94530a92..07ce0d5a8fa6 100644
--- a/t/APISIX.pm
+++ b/t/APISIX.pm
@@ -259,6 +259,18 @@ my $disable_proxy_buffering_location = <<_EOC_;
}
_EOC_
+my $websocket_location = <<_EOC_;
+ location \@websocket_pass {
+ content_by_lua_block {
+ apisix.websocket_content_phase()
+ }
+
+ log_by_lua_block {
+ apisix.websocket_log_phase()
+ }
+ }
+_EOC_
+
my $a6_ngx_directives = "";
if ($version =~ m/\/apisix-nginx-module/) {
$a6_ngx_directives = <<_EOC_;
@@ -775,6 +787,20 @@ _EOC_
}
}
+ # accepts a connection on any path but never writes a response, so a
+ # client waiting on it reliably times out instead of being refused or
+ # having to depend on an unroutable address actually hanging
+ server {
+ listen 1986;
+ server_tokens off;
+
+ location / {
+ content_by_lua_block {
+ ngx.sleep(30)
+ }
+ }
+ }
+
$a6_ngx_directives
server {
@@ -1008,6 +1034,7 @@ _EOC_
$grpc_location
$dubbo_location
$disable_proxy_buffering_location
+ $websocket_location
location = /proxy_mirror {
internal;
diff --git a/t/lib/server.lua b/t/lib/server.lua
index c21975ff6691..757c3c584acb 100644
--- a/t/lib/server.lua
+++ b/t/lib/server.lua
@@ -389,6 +389,225 @@ end
_M.websocket_handshake_route = _M.websocket_handshake
+-- Echoes every text/binary frame it receives back to the sender unchanged,
+-- so a fronting proxy's frame-level plugin hooks can be observed by diffing
+-- what the client sent against what it gets back. Used by the
+-- websocket-enhanced (ws/wss upstream scheme) test suite.
+function _M.websocket_echo()
+ local websocket = require "resty.websocket.server"
+ local wb, err = websocket:new()
+ if not wb then
+ ngx.log(ngx.ERR, "failed to new websocket: ", err)
+ return ngx.exit(400)
+ end
+
+ while true do
+ local data, typ, err = wb:recv_frame()
+ if not data then
+ if err and err:find("timeout", 1, true) then
+ goto continue
+ end
+ ngx.log(ngx.ERR, "failed to receive frame: ", err)
+ return
+ end
+
+ if typ == "close" then
+ wb:send_close(1000, "")
+ return
+ elseif typ == "ping" then
+ wb:send_pong(data)
+ elseif typ == "text" or typ == "binary" then
+ local send = typ == "text" and wb.send_text or wb.send_binary
+ local bytes, send_err = send(wb, data)
+ if not bytes then
+ ngx.log(ngx.ERR, "failed to echo frame: ", send_err)
+ return
+ end
+ end
+
+ ::continue::
+ end
+end
+
+
+-- Like websocket_echo, but the first thing it sends back is a text frame
+-- carrying the request URI (with query string) it was actually dispatched
+-- with, so a test can confirm what path/query a fronting proxy forwarded.
+-- Falls into the same echo loop afterwards.
+function _M.websocket_echo_uri()
+ local websocket = require "resty.websocket.server"
+ local wb, err = websocket:new()
+ if not wb then
+ ngx.log(ngx.ERR, "failed to new websocket: ", err)
+ return ngx.exit(400)
+ end
+
+ local bytes, send_err = wb:send_text(ngx.var.request_uri)
+ if not bytes then
+ ngx.log(ngx.ERR, "failed to send request_uri: ", send_err)
+ return
+ end
+
+ while true do
+ local data, typ, recv_err = wb:recv_frame()
+ if not data then
+ if recv_err and recv_err:find("timeout", 1, true) then
+ goto continue
+ end
+ ngx.log(ngx.ERR, "failed to receive frame: ", recv_err)
+ return
+ end
+
+ if typ == "close" then
+ wb:send_close(1000, "")
+ return
+ elseif typ == "ping" then
+ wb:send_pong(data)
+ elseif typ == "text" or typ == "binary" then
+ local send = typ == "text" and wb.send_text or wb.send_binary
+ local ok, echo_err = send(wb, data)
+ if not ok then
+ ngx.log(ngx.ERR, "failed to echo frame: ", echo_err)
+ return
+ end
+ end
+
+ ::continue::
+ end
+end
+
+
+-- Like websocket_echo, but the first thing it sends back is a text frame
+-- carrying the X-Real-IP/X-Forwarded-For it actually received as JSON, so a
+-- test can confirm what a fronting proxy set them to. Falls into the same
+-- echo loop afterwards.
+function _M.websocket_echo_headers()
+ local websocket = require "resty.websocket.server"
+ local wb, err = websocket:new()
+ if not wb then
+ ngx.log(ngx.ERR, "failed to new websocket: ", err)
+ return ngx.exit(400)
+ end
+
+ local headers = ngx.req.get_headers()
+ local bytes, send_err = wb:send_text(json_encode({
+ x_real_ip = headers["X-Real-IP"],
+ x_forwarded_for = headers["X-Forwarded-For"],
+ }))
+ if not bytes then
+ ngx.log(ngx.ERR, "failed to send headers: ", send_err)
+ return
+ end
+
+ while true do
+ local data, typ, recv_err = wb:recv_frame()
+ if not data then
+ if recv_err and recv_err:find("timeout", 1, true) then
+ goto continue
+ end
+ ngx.log(ngx.ERR, "failed to receive frame: ", recv_err)
+ return
+ end
+
+ if typ == "close" then
+ wb:send_close(1000, "")
+ return
+ elseif typ == "ping" then
+ wb:send_pong(data)
+ elseif typ == "text" or typ == "binary" then
+ local send = typ == "text" and wb.send_text or wb.send_binary
+ local ok, echo_err = send(wb, data)
+ if not ok then
+ ngx.log(ngx.ERR, "failed to echo frame: ", echo_err)
+ return
+ end
+ end
+
+ ::continue::
+ end
+end
+
+
+-- Sends one fragmented text message ("hello " + "world" as two continuation
+-- frames) right after the handshake, to verify a fronting proxy's
+-- aggregate_fragments option reassembles it into a single frame instead of
+-- forwarding (or invoking frame hooks on) two separate pieces.
+function _M.websocket_fragment()
+ local websocket = require "resty.websocket.server"
+ local wb, err = websocket:new()
+ if not wb then
+ ngx.log(ngx.ERR, "failed to new websocket: ", err)
+ return ngx.exit(400)
+ end
+
+ local ok, send_err = wb:send_frame(false, 0x1, "hello ")
+ if not ok then
+ ngx.log(ngx.ERR, "failed to send first fragment: ", send_err)
+ return
+ end
+
+ ok, send_err = wb:send_frame(true, 0x0, "world")
+ if not ok then
+ ngx.log(ngx.ERR, "failed to send final fragment: ", send_err)
+ return
+ end
+
+ -- drain until the client closes, so the connection doesn't just vanish
+ -- out from under the proxy mid-test
+ while true do
+ local data, typ, recv_err = wb:recv_frame()
+ if not data then
+ if recv_err and recv_err:find("timeout", 1, true) then
+ goto continue
+ end
+ return
+ end
+ if typ == "close" then
+ wb:send_close(1000, "")
+ return
+ end
+ ::continue::
+ end
+end
+
+
+-- Sends a close frame of its own right after the handshake, without waiting
+-- for the client to initiate one, to exercise an upstream-initiated close.
+function _M.websocket_close_upstream_initiated()
+ local websocket = require "resty.websocket.server"
+ local wb, err = websocket:new()
+ if not wb then
+ ngx.log(ngx.ERR, "failed to new websocket: ", err)
+ return ngx.exit(400)
+ end
+
+ wb:send_close(1000, "bye")
+end
+
+
+-- Completes the handshake, echoes exactly one frame, then vanishes without
+-- sending a close frame, to simulate an upstream that dies mid-session
+-- instead of closing cleanly.
+function _M.websocket_abrupt_close()
+ local websocket = require "resty.websocket.server"
+ local wb, err = websocket:new()
+ if not wb then
+ ngx.log(ngx.ERR, "failed to new websocket: ", err)
+ return ngx.exit(400)
+ end
+
+ local data, typ = wb:recv_frame()
+ if data and (typ == "text" or typ == "binary") then
+ local send = typ == "text" and wb.send_text or wb.send_binary
+ send(wb, data)
+ end
+
+ -- returning here, with the connection already hijacked by
+ -- resty.websocket.server, drops the raw TCP connection without a
+ -- close handshake
+end
+
+
-- keep the session open until the peer goes away, so that the request stays in
-- flight in the balancer the way a real WebSocket session does. An idle timeout is
-- the normal state of such a session, not an error: keep waiting, and only give up
diff --git a/t/node/websocket-proxy.spec.mts b/t/node/websocket-proxy.spec.mts
new file mode 100644
index 000000000000..7b85d68699e2
--- /dev/null
+++ b/t/node/websocket-proxy.spec.mts
@@ -0,0 +1,479 @@
+/*
+ * Licensed to the Apache Software Foundation (ASF) under one or more
+ * contributor license agreements. See the NOTICE file distributed with
+ * this work for additional information regarding copyright ownership.
+ * The ASF licenses this file to You under the Apache License, Version 2.0
+ * (the "License"); you may not use this file except in compliance with
+ * the License. You may obtain a copy of the License at
+ *
+ * http://www.apache.org/licenses/LICENSE-2.0
+ *
+ * Unless required by applicable law or agreed to in writing, software
+ * distributed under the License is distributed on an "AS IS" BASIS,
+ * WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or implied.
+ * See the License for the specific language governing permissions and
+ * limitations under the License.
+ */
+import { describe, expect, it, jest } from '@jest/globals';
+import axios from 'axios';
+import WS from 'ws';
+
+import { request as requestAdminAPI } from '../ts/admin_api';
+import { wait } from '../ts/utils';
+
+// Every test here does at least one real websocket handshake plus etcd sync
+// round trip, which the shared 5s Jest default leaves little room for on a
+// loaded machine; the handful of tests that need more than this still set
+// their own per-test timeout on top of it.
+jest.setTimeout(15000);
+
+const PROXY_BASE = 'ws://localhost:1984';
+// a loopback address nothing listens on, used as an unreachable upstream node
+const DEAD_NODE = '127.0.0.1:1';
+const DEAD_NODE_2 = '127.0.0.1:2';
+// accepts the connection but never responds, so it reliably exercises the
+// "timeout" (504) branch instead of "tcp failure" - unlike an unroutable
+// address, this doesn't depend on how a given network treats one
+const BLACKHOLE_NODE = '127.0.0.1:1986';
+const ECHO_NODE = '127.0.0.1:1980';
+
+let nextRouteId = 1;
+
+// Routes with a URI no other test in this file reuses can just be created
+// once and left behind (the whole test-nginx instance goes away at the end
+// of the run anyway).
+const createRoute = async (
+ path: string,
+ upstream: object,
+ plugins?: object,
+) => {
+ const id = `ws-proxy-${nextRouteId++}`;
+ const res = await requestAdminAPI(`/apisix/admin/routes/${id}`, 'PUT', {
+ uri: path,
+ upstream,
+ plugins,
+ });
+ expect(res.status).toBe(res.status < 300 ? res.status : 200);
+ // give etcd -> apisix config sync a moment to land before the first request
+ await wait(300);
+ return id;
+};
+
+// Most tests below share the /websocket_echo URI across very different
+// upstream/plugin configs. Deleting and recreating a route under the same
+// URI between tests leaves a window where the delete has been sent but
+// hasn't synced yet when the next test's create lands, and the two can race
+// - the client then gets whichever half-applied state the router held at
+// that instant. PUTting the same fixed route id instead is a plain
+// overwrite, so there's no delete in flight to race with.
+const ECHO_ROUTE_ID = 'ws-proxy-echo';
+const putEchoRoute = async (upstream: object, plugins?: object) => {
+ const res = await requestAdminAPI(`/apisix/admin/routes/${ECHO_ROUTE_ID}`, 'PUT', {
+ uri: '/websocket_echo',
+ upstream,
+ plugins,
+ });
+ expect(res.status).toBe(res.status < 300 ? res.status : 200);
+ await wait(300);
+};
+
+// Opens a websocket connection, sends one text frame, resolves with the
+// first frame received in reply (or rejects on error/close-before-reply).
+const sendAndReceive = (path: string, payload: string) =>
+ new Promise
((resolve, reject) => {
+ const ws = new WebSocket(`${PROXY_BASE}${path}`);
+ ws.addEventListener('open', () => ws.send(payload));
+ ws.addEventListener('message', (ev) => {
+ resolve(ev.data as string);
+ ws.close();
+ });
+ ws.addEventListener('error', (ev) =>
+ reject(new Error((ev as unknown as { message?: string }).message ?? 'websocket error')),
+ );
+ });
+
+// Resolves with the close event's code. onOpen fires right after connecting,
+// so it can send a frame or otherwise trigger whatever leads to the close.
+//
+// The WebSocket spec requires an abnormal closure to fire an error event
+// before its close event, not instead of it, so an expected-to-fail
+// connection (tolerateError: true) must not treat that error as a failure
+// and must instead keep waiting for the close event that follows it.
+const waitForClose = (
+ path: string,
+ onOpen?: (ws: WebSocket) => void,
+ tolerateError = false,
+) =>
+ new Promise((resolve, reject) => {
+ const ws = new WebSocket(`${PROXY_BASE}${path}`);
+ ws.addEventListener('open', () => onOpen?.(ws));
+ ws.addEventListener('close', (ev) => resolve(ev.code));
+ ws.addEventListener('error', (ev) => {
+ if (!tolerateError) {
+ reject(new Error((ev as unknown as { message?: string }).message ?? 'websocket error'));
+ }
+ });
+ });
+
+describe('websocket-proxy (ws/wss upstream scheme)', () => {
+ describe('frame-level plugin hooks', () => {
+ it('lets a plugin rewrite the client frame before it reaches the upstream, and the upstream frame before it reaches the client', async () => {
+ await putEchoRoute(
+ { type: 'roundrobin', scheme: 'ws', nodes: { [ECHO_NODE]: 1 } },
+ {
+ // example-plugin's ws_client_frame/ws_upstream_frame hooks append
+ // "-client"/"-upstream" to every text frame they see, in-flight.
+ 'example-plugin': { i: 1 },
+ },
+ );
+
+ // the echo backend bounces whatever it received back unchanged, so the
+ // round trip proves both directions were actually rewritten in flight.
+ const reply = await sendAndReceive('/websocket_echo', 'hello');
+ expect(reply).toBe('hello-client-upstream');
+ });
+
+ it('does not touch binary frames (the hooks only rewrite text frames)', async () => {
+ await putEchoRoute(
+ { type: 'roundrobin', scheme: 'ws', nodes: { [ECHO_NODE]: 1 } },
+ { 'example-plugin': { i: 1 } },
+ );
+
+ const reply = await new Promise((resolve, reject) => {
+ const ws = new WebSocket(`${PROXY_BASE}/websocket_echo`);
+ ws.binaryType = 'arraybuffer';
+ ws.addEventListener('open', () => ws.send(new Uint8Array([1, 2, 3, 4])));
+ ws.addEventListener('message', (ev) => {
+ resolve(ev.data as ArrayBuffer);
+ ws.close();
+ });
+ ws.addEventListener('error', (ev) =>
+ reject(new Error((ev as unknown as { message?: string }).message ?? 'websocket error')),
+ );
+ });
+ expect(new Uint8Array(reply)).toEqual(new Uint8Array([1, 2, 3, 4]));
+ });
+ });
+
+ describe('fragmented frames', () => {
+ it('reassembles a fragmented message into one frame before invoking plugin hooks', async () => {
+ await createRoute('/websocket_fragment', {
+ type: 'roundrobin',
+ scheme: 'ws',
+ nodes: { [ECHO_NODE]: 1 },
+ }, {
+ 'example-plugin': { i: 1 },
+ });
+
+ // websocket_fragment sends "hello " and "world" as two continuation
+ // frames of the same message; if aggregate_fragments works, the client
+ // (and the ws_upstream_frame hook in between) see exactly one frame
+ // with the joined payload, not two separate ones.
+ const messages: string[] = [];
+ await new Promise((resolve, reject) => {
+ const ws = new WebSocket(`${PROXY_BASE}/websocket_fragment`);
+ ws.addEventListener('message', (ev) => {
+ messages.push(ev.data as string);
+ ws.close();
+ });
+ ws.addEventListener('close', () => resolve());
+ ws.addEventListener('error', (ev) =>
+ reject(new Error((ev as unknown as { message?: string }).message ?? 'websocket error')),
+ );
+ });
+ expect(messages).toEqual(['hello world-upstream']);
+ });
+ });
+
+ describe('ping/pong', () => {
+ it('forwards a client ping to the upstream and the upstream pong back to the client', async () => {
+ await putEchoRoute({ type: 'roundrobin', scheme: 'ws', nodes: { [ECHO_NODE]: 1 } });
+
+ await new Promise((resolve, reject) => {
+ const ws = new WS(`${PROXY_BASE}/websocket_echo`);
+ ws.on('open', () => ws.ping());
+ ws.on('pong', () => {
+ ws.terminate();
+ resolve();
+ });
+ ws.on('error', reject);
+ });
+ });
+ });
+
+ describe('close handshake', () => {
+ it('lets the client close cleanly and the upstream echoes the close code back', async () => {
+ await putEchoRoute({ type: 'roundrobin', scheme: 'ws', nodes: { [ECHO_NODE]: 1 } });
+
+ const code = await waitForClose('/websocket_echo', (ws) => ws.close(1000, 'bye'));
+ expect(code).toBe(1000);
+ });
+
+ it('forwards an upstream-initiated close to the client', async () => {
+ await createRoute('/websocket_close_upstream_initiated', {
+ type: 'roundrobin',
+ scheme: 'ws',
+ nodes: { [ECHO_NODE]: 1 },
+ });
+
+ const code = await waitForClose('/websocket_close_upstream_initiated');
+ expect(code).toBe(1000);
+ });
+ });
+
+ describe('abrupt disconnects', () => {
+ it('reports an abnormal closure (1006) to the client when the upstream vanishes mid-session', async () => {
+ await createRoute('/websocket_abrupt_close', {
+ type: 'roundrobin',
+ scheme: 'ws',
+ nodes: { [ECHO_NODE]: 1 },
+ });
+
+ const code = await waitForClose('/websocket_abrupt_close', (ws) => ws.send('hi'), true);
+ expect(code).toBe(1006);
+ });
+
+ it('cleans up the upstream side when the client vanishes without closing', async () => {
+ await putEchoRoute({ type: 'roundrobin', scheme: 'ws', nodes: { [ECHO_NODE]: 1 } });
+
+ const activeConnections = async () => {
+ const res = await axios.get('http://localhost:1984/apisix/nginx_status');
+ const match = /Active connections:\s*(\d+)/.exec(res.data as string);
+ return match ? Number(match[1]) : NaN;
+ };
+
+ const baseline = await activeConnections();
+
+ // open and forcibly kill a handful of connections without a close
+ // handshake (ws's .terminate() drops the TCP connection directly,
+ // which the standard WebSocket API has no equivalent for)
+ for (let i = 0; i < 10; i++) {
+ await new Promise((resolve, reject) => {
+ const ws = new WS(`${PROXY_BASE}/websocket_echo`);
+ ws.on('open', () => {
+ ws.terminate();
+ resolve();
+ });
+ ws.on('error', reject);
+ });
+ }
+
+ // give the proxy's forwarder coroutines a moment to notice the dead
+ // sockets and tear themselves down
+ await wait(1000);
+
+ const after = await activeConnections();
+ // a leak would grow roughly linearly with the number of terminated
+ // connections (10 here); allow some slack for unrelated background
+ // activity in the shared test-nginx instance instead of an exact match
+ expect(after).toBeLessThan(baseline + 5);
+ }, 10000);
+ });
+
+ describe('upstream retry', () => {
+ it('retries the next node when the first one refuses the connection', async () => {
+ await putEchoRoute({
+ type: 'roundrobin',
+ scheme: 'ws',
+ retries: 3,
+ nodes: { [DEAD_NODE]: 100, [ECHO_NODE]: 1 },
+ });
+
+ const reply = await sendAndReceive('/websocket_echo', 'hello');
+ expect(reply).toBe('hello');
+ });
+
+ it('returns 502 once every node has been tried and failed', async () => {
+ await putEchoRoute({
+ type: 'roundrobin',
+ scheme: 'ws',
+ retries: 2,
+ nodes: { [DEAD_NODE]: 1, [DEAD_NODE_2]: 1 },
+ });
+
+ await expect(
+ axios.get('http://localhost:1984/websocket_echo', {
+ headers: {
+ Connection: 'Upgrade',
+ Upgrade: 'websocket',
+ 'Sec-WebSocket-Key': 'dGhlIHNhbXBsZSBub25jZQ==',
+ 'Sec-WebSocket-Version': '13',
+ },
+ }),
+ ).rejects.toMatchObject({
+ response: { status: 502 },
+ });
+ });
+
+ it('retries past a connect timeout, not just a refused connection', async () => {
+ await putEchoRoute({
+ type: 'roundrobin',
+ scheme: 'ws',
+ retries: 2,
+ timeout: { connect: 1, send: 5, read: 5 },
+ nodes: { [BLACKHOLE_NODE]: 100, [ECHO_NODE]: 1 },
+ });
+
+ const start = Date.now();
+ const reply = await sendAndReceive('/websocket_echo', 'hello');
+ const elapsed = Date.now() - start;
+ expect(reply).toBe('hello');
+ // an instant refusal (tcp_failure) would resolve in a few ms; only a
+ // real connect timeout takes close to the configured 1s
+ expect(elapsed).toBeGreaterThanOrEqual(900);
+ }, 10000);
+
+ it('retries across more than one dead node before reaching a healthy one', async () => {
+ await putEchoRoute({
+ type: 'roundrobin',
+ scheme: 'ws',
+ retries: 3,
+ nodes: { [DEAD_NODE]: 100, [DEAD_NODE_2]: 100, [ECHO_NODE]: 1 },
+ });
+
+ const reply = await sendAndReceive('/websocket_echo', 'hello');
+ expect(reply).toBe('hello');
+ });
+
+ it('retries the same way for a least_conn upstream, not just roundrobin', async () => {
+ await putEchoRoute({
+ type: 'least_conn',
+ scheme: 'ws',
+ retries: 3,
+ nodes: { [DEAD_NODE]: 100, [ECHO_NODE]: 1 },
+ });
+
+ const reply = await sendAndReceive('/websocket_echo', 'hello');
+ expect(reply).toBe('hello');
+ });
+ });
+
+ describe('passive health check', () => {
+ it('marks a node unhealthy after enough failed connection attempts', async () => {
+ await putEchoRoute({
+ type: 'roundrobin',
+ scheme: 'ws',
+ retries: 1,
+ nodes: { [DEAD_NODE]: 1, [ECHO_NODE]: 1 },
+ checks: {
+ active: { type: 'tcp', http_path: '/', timeout: 1, healthy: { interval: 1 } },
+ passive: { unhealthy: { tcp_failures: 1 } },
+ },
+ });
+
+ // one connect attempt is enough to report a tcp failure for DEAD_NODE
+ await sendAndReceive('/websocket_echo', 'hello');
+
+ let unhealthyFound = false;
+ for (let i = 0; i < 10 && !unhealthyFound; i++) {
+ await wait(500);
+ const res = await requestAdminAPI(`/v1/healthcheck/routes/${ECHO_ROUTE_ID}`);
+ const { nodes } = res.data as { nodes: { ip: string; port: number; status: string }[] };
+ unhealthyFound = nodes.some((n) => n.port === 1 && n.status !== 'healthy');
+ }
+
+ expect(unhealthyFound).toBe(true);
+ }, 15000);
+ });
+
+ describe('upstream URI forwarding', () => {
+ it("forwards the client's request URI, including the query string", async () => {
+ await createRoute('/websocket_echo_uri', {
+ type: 'roundrobin',
+ scheme: 'ws',
+ nodes: { [ECHO_NODE]: 1 },
+ });
+
+ const reply = await new Promise((resolve, reject) => {
+ const ws = new WebSocket(`${PROXY_BASE}/websocket_echo_uri?foo=bar`);
+ ws.addEventListener('message', (ev) => {
+ resolve(ev.data as string);
+ ws.close();
+ });
+ ws.addEventListener('error', (ev) =>
+ reject(new Error((ev as unknown as { message?: string }).message ?? 'websocket error')),
+ );
+ });
+ expect(reply).toBe('/websocket_echo_uri?foo=bar');
+ });
+
+ it("forwards the proxy-rewrite plugin's rewritten URI instead of the original one", async () => {
+ await createRoute(
+ '/websocket_proxy_rewrite_uri',
+ {
+ type: 'roundrobin',
+ scheme: 'ws',
+ nodes: { [ECHO_NODE]: 1 },
+ },
+ {
+ 'proxy-rewrite': { uri: '/websocket_echo_uri' },
+ },
+ );
+
+ const reply = await new Promise((resolve, reject) => {
+ const ws = new WebSocket(`${PROXY_BASE}/websocket_proxy_rewrite_uri`);
+ ws.addEventListener('message', (ev) => {
+ resolve(ev.data as string);
+ ws.close();
+ });
+ ws.addEventListener('error', (ev) =>
+ reject(new Error((ev as unknown as { message?: string }).message ?? 'websocket error')),
+ );
+ });
+ expect(reply).toBe('/websocket_echo_uri');
+ });
+ });
+
+ describe('client address headers', () => {
+ it('overrides X-Real-IP and appends this hop to X-Forwarded-For, not what the client sent', async () => {
+ await createRoute('/websocket_echo_headers', {
+ type: 'roundrobin',
+ scheme: 'ws',
+ nodes: { [ECHO_NODE]: 1 },
+ });
+
+ // connect via the literal loopback address, not PROXY_BASE's
+ // "localhost", so $remote_addr is deterministically 127.0.0.1
+ const reply = await new Promise((resolve, reject) => {
+ const ws = new WS('ws://127.0.0.1:1984/websocket_echo_headers', {
+ headers: { 'X-Real-IP': '1.2.3.4', 'X-Forwarded-For': '5.6.7.8' },
+ });
+ ws.on('message', (data) => {
+ resolve(data.toString());
+ ws.close();
+ });
+ ws.on('error', reject);
+ });
+
+ const seen = JSON.parse(reply);
+ expect(seen.x_real_ip).toBe('127.0.0.1');
+ expect(seen.x_forwarded_for).toBe('5.6.7.8, 127.0.0.1');
+ });
+ });
+
+ describe('concurrent connections', () => {
+ it("keeps two simultaneous connections' frame data isolated from each other", async () => {
+ await putEchoRoute(
+ { type: 'roundrobin', scheme: 'ws', nodes: { [ECHO_NODE]: 1 } },
+ { 'example-plugin': { i: 1 } },
+ );
+
+ const open = (payload: string) =>
+ new Promise((resolve, reject) => {
+ const ws = new WebSocket(`${PROXY_BASE}/websocket_echo`);
+ ws.addEventListener('open', () => ws.send(payload));
+ ws.addEventListener('message', (ev) => {
+ resolve(ev.data as string);
+ ws.close();
+ });
+ ws.addEventListener('error', (ev) =>
+ reject(new Error((ev as unknown as { message?: string }).message ?? 'websocket error')),
+ );
+ });
+
+ const [replyA, replyB] = await Promise.all([open('alpha'), open('beta')]);
+ expect(replyA).toBe('alpha-client-upstream');
+ expect(replyB).toBe('beta-client-upstream');
+ });
+ });
+});
diff --git a/t/node/websocket-proxy.t b/t/node/websocket-proxy.t
new file mode 100644
index 000000000000..73b8fe9251c6
--- /dev/null
+++ b/t/node/websocket-proxy.t
@@ -0,0 +1,35 @@
+#
+# Licensed to the Apache Software Foundation (ASF) under one or more
+# contributor license agreements. See the NOTICE file distributed with
+# this work for additional information regarding copyright ownership.
+# The ASF licenses this file to You under the Apache License, Version 2.0
+# (the "License"); you may not use this file except in compliance with
+# the License. You may obtain a copy of the License at
+#
+# http://www.apache.org/licenses/LICENSE-2.0
+#
+# Unless required by applicable law or agreed to in writing, software
+# distributed under the License is distributed on an "AS IS" BASIS,
+# WITHOUT WARRANTIES OR CONDITIONS OF ANY KIND, either express or implied.
+# See the License for the specific language governing permissions and
+# limitations under the License.
+#
+use t::APISIX 'no_plan';
+
+repeat_each(1);
+no_long_string();
+no_root_location();
+
+run_tests();
+
+__DATA__
+
+=== TEST 1: test
+--- timeout: 60
+--- max_size: 2048000
+--- exec
+cd t && pnpm test node/websocket-proxy.spec.mts 2>&1
+--- no_error_log
+failed to execute the script with status
+--- response_body eval
+qr/PASS node\/websocket-proxy.spec.mts/
diff --git a/t/package.json b/t/package.json
index 7661c6eabaca..948dd9cba015 100644
--- a/t/package.json
+++ b/t/package.json
@@ -12,6 +12,7 @@
"@types/google-protobuf": "^3.15.12",
"@types/jest": "29.5.14",
"@types/node": "22.14.1",
+ "@types/ws": "^8.18.1",
"axios": "^1.16.0",
"docker-compose": "^1.2.0",
"google-protobuf": "^3.21.4",
@@ -23,6 +24,7 @@
"simple-git": "^3.27.0",
"ts-jest": "29.3.2",
"ts-node": "10.9.2",
+ "ws": "^8.21.3",
"xhr2": "^0.2.1",
"yaml": "^2.7.1"
},
diff --git a/t/pnpm-lock.yaml b/t/pnpm-lock.yaml
index 46bedf29a19c..6e8ca05578d4 100644
--- a/t/pnpm-lock.yaml
+++ b/t/pnpm-lock.yaml
@@ -32,6 +32,9 @@ importers:
'@types/node':
specifier: 22.14.1
version: 22.14.1
+ '@types/ws':
+ specifier: ^8.18.1
+ version: 8.18.1
axios:
specifier: ^1.16.0
version: 1.16.0
@@ -65,6 +68,9 @@ importers:
ts-node:
specifier: 10.9.2
version: 10.9.2(@types/node@22.14.1)(typescript@5.8.3)
+ ws:
+ specifier: ^8.21.3
+ version: 8.21.3
xhr2:
specifier: ^0.2.1
version: 0.2.1
@@ -509,6 +515,9 @@ packages:
'@types/stack-utils@2.0.3':
resolution: {integrity: sha512-9aEbYZ3TbYMznPdcdr3SmIrLXwC/AKZXQeCf9Pgao5CKb8CyHuEX5jzWPTkvregvhRJHcpRO6BFoGW9ycaOkYw==}
+ '@types/ws@8.18.1':
+ resolution: {integrity: sha512-ThVF6DCVhA8kUGy+aazFQ4kXQ7E1Ty7A3ypFOe0IcJV8O/M511G99AW24irKrW56Wt44yG9+ij8FaqoBGkuBXg==}
+
'@types/yargs-parser@21.0.3':
resolution: {integrity: sha512-I4q9QU9MQv4oEOz4tAHJtNz1cwuLxn2F3xcc2iV5WdqLPpUnj30aUuxt1mAxYTG+oe8CZMV/+6rU4S4gRDzqtQ==}
@@ -1764,6 +1773,18 @@ packages:
resolution: {integrity: sha512-7KxauUdBmSdWnmpaGFg+ppNjKF8uNLry8LyzjauQDOVONfFLNKrKvQOxZ/VuTIcS/gge/YNahf5RIIQWTSarlg==}
engines: {node: ^12.13.0 || ^14.15.0 || >=16.0.0}
+ ws@8.21.3:
+ resolution: {integrity: sha512-201TZ/kPWxoPr/OKWjquZR1SWKXcvxdH+e1xrx89b3YbmzLMFCLfnaG1HFIgWzJOEWZ7MvpK++odZufgYR50Rw==}
+ engines: {node: '>=10.0.0'}
+ peerDependencies:
+ bufferutil: ^4.0.1
+ utf-8-validate: '>=5.0.2'
+ peerDependenciesMeta:
+ bufferutil:
+ optional: true
+ utf-8-validate:
+ optional: true
+
xhr2@0.2.1:
resolution: {integrity: sha512-sID0rrVCqkVNUn8t6xuv9+6FViXjUVXq8H5rWOH2rz9fDNQEd4g0EA2XlcEdJXRz5BMEn4O1pJFdT+z4YHhoWw==}
engines: {node: '>= 6'}
@@ -2402,6 +2423,10 @@ snapshots:
'@types/stack-utils@2.0.3': {}
+ '@types/ws@8.18.1':
+ dependencies:
+ '@types/node': 22.14.1
+
'@types/yargs-parser@21.0.3': {}
'@types/yargs@17.0.33':
@@ -3792,6 +3817,8 @@ snapshots:
imurmurhash: 0.1.4
signal-exit: 3.0.7
+ ws@8.21.3: {}
+
xhr2@0.2.1: {}
y18n@5.0.8: {}